Towards a Unified Framework for Cybersecurity and AI Safety: Recommendations for Secure Development of Large Language Models
Lexley Maree Villasis, Srishti Dutta, Yohan Mathew · Team SLAY
Submitted to AI Policy Hackathon at Johns Hopkins University. Sprint projects are early-stage work by participants, not Apart Research publications.
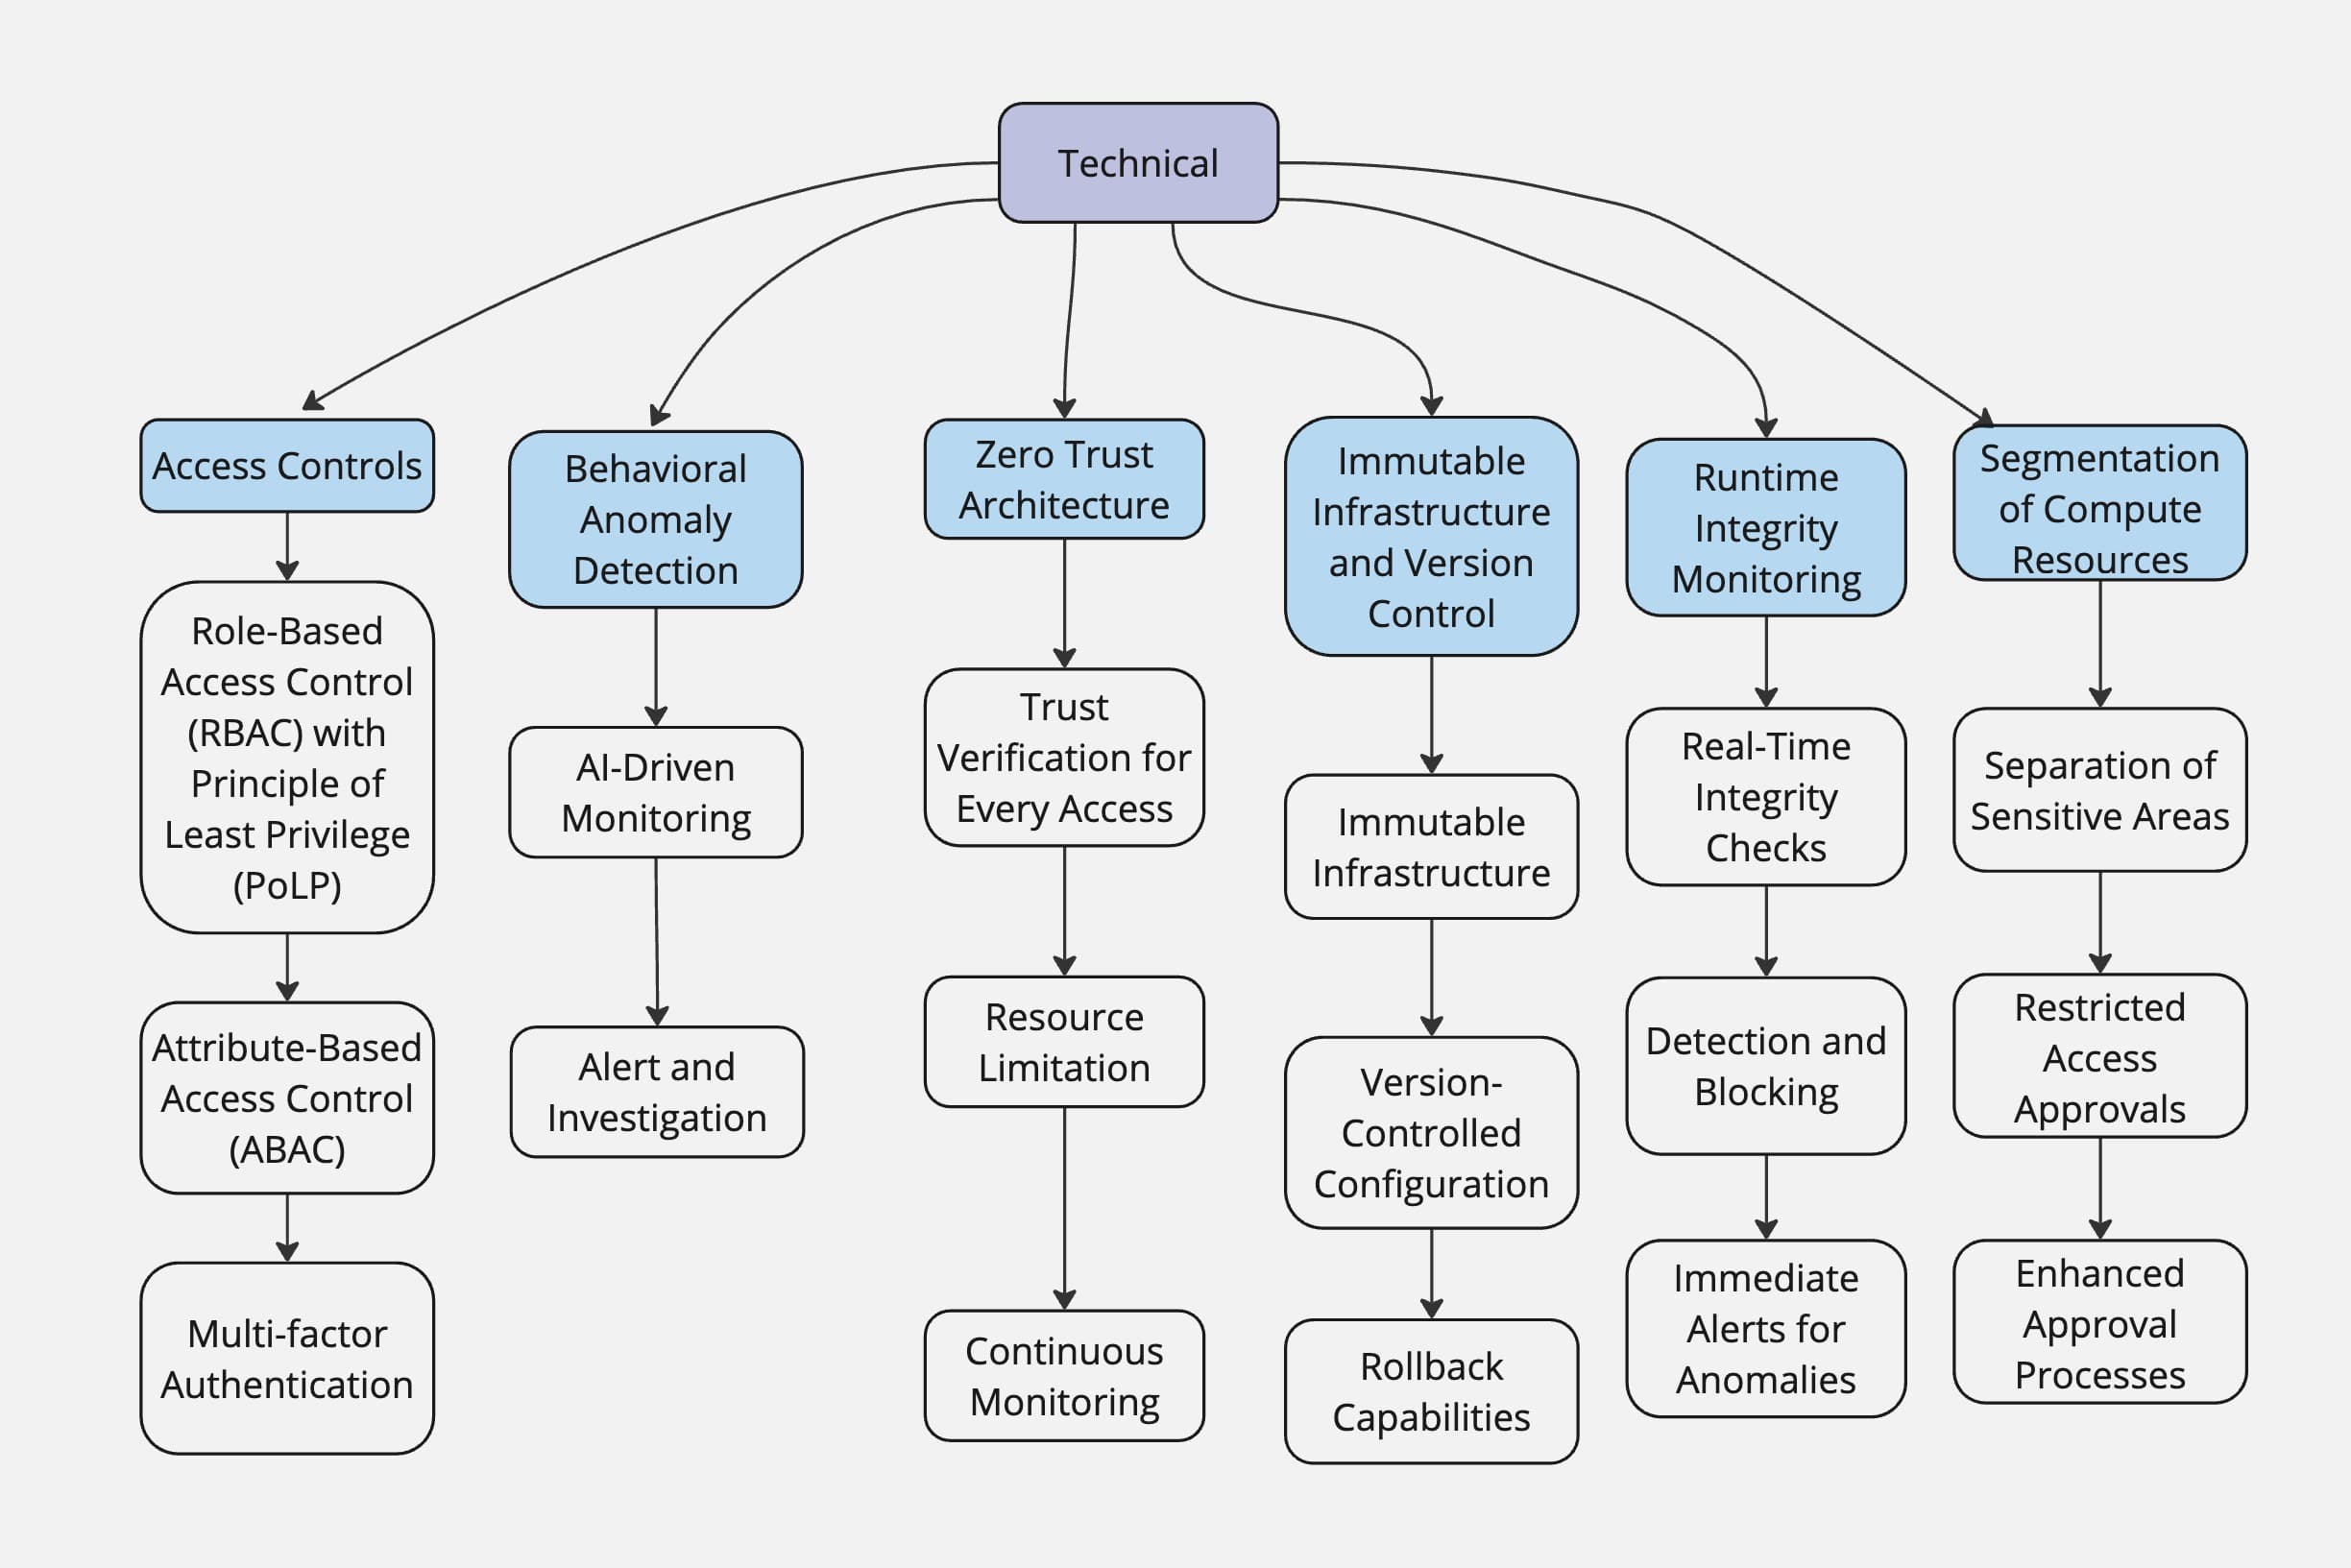
By analyzing the recent incident involving a ByteDance intern, we highlight the urgent need for robust security measures to protect AI infrastructure and sensitive data. We propose ae a comprehensive framework that integrates technical, internal, and international approaches to mitigate risks.
Reviews
Emphasizing the prevention of insider threats is a great point. the proposal might face implementation challenges. could benefit from a stronger focus on ethical considerations and public engagement for broader acceptance
I thought this aptly adressed a growing problem concerning the vunerability of critical infrastructure in the U.S. The paper however, only frames the problem in terms of one incident and doesn't present an implementation mechanism.
Cite this project
@misc{villasis2024towards,
  title = {{Towards a Unified Framework for Cybersecurity and AI Safety: Recommendations for Secure Development of Large Language Models}},
  author = {Lexley Maree Villasis and Srishti Dutta and Yohan Mathew},
  year = {2024},
  month = oct,
  note = {Submitted to AI Policy Hackathon at Johns Hopkins University, an Apart Research Sprint},
  howpublished = {\url{https://apartresearch.com/sprints/projects/towards-a-unified-framework-for-cybersecurity-and-ai-safety-recommendations-for-secure-development-of-large-language-models}},
  url = {https://apartresearch.com/sprints/projects/towards-a-unified-framework-for-cybersecurity-and-ai-safety-recommendations-for-secure-development-of-large-language-models}
}
More from AI Policy Hackathon at Johns Hopkins University
- 1st place by peer reviewView project: Robust Machine Unlearning for Dangerous Capabilities
Robust Machine Unlearning for Dangerous Capabilities
Robust Machine Unlearning for Dangerous Capabilities
We test different unlearning methods to make models more robust against exploitation by malicious actors for the creation of bioweapons.
- View project: Infectious Disease Outbreak Prediction and Dashboard
Infectious Disease Outbreak Prediction and Dashboard
Infectious Diseace Dashboards
Our project developed an interactive dashboard to monitor, visualize, and analyze infectious disease outbreaks worldwide. It consolidates historical data from sources like WHO, OWID, and CDC for diseases including …
- View project: Modernizing DC’s Emergency Communications
Modernizing DC’s Emergency Communications
AI-CAD
The District of Columbia proposes implementing an AI-enabled Computer-Aided Dispatch (CAD) system to address critical deficiencies in our current emergency alert infrastructure. This policy establishes a framework for …